Free Two people analyzing business graphs and documents at an office desk. Stock Photo

What to Ask a Software Vendor AfterThey Report a Data Breach

Article Summary: Confirm that the notice is genuine, then ask whether your business was affected, what information was exposed, when the breach happened, and whether any passwords, access tokens, or connected systems need attention. Keep written records of the vendor’s answers and involve your IT provider, insurer, or legal adviser when needed.

You’ve just found yourself on the receiving end of a data breach notice from one of your software vendors.

Maybe it’s the company that handles your payroll. It could be your accounting platform, CRM, cloud storage provider, or another service your team uses every day.

The email says the vendor discovered a security incident and has started an investigation. It may say that certain systems were accessed or that the incident has been contained. Then it gives you a support address and promises further updates.

But you’re left with a question the notice may not answer: What does this mean for your business?

The first notice often arrives before the vendor knows the full extent of the breach. Its security team may still be reviewing logs, identifying affected systems, and confirming what information was accessed. That takes time, but you may need to reset accounts, check transactions, warn staff, or contact your insurer before the investigation is finished.

You don’t have to wait for the final report before asking questions. Confirm that the notice is genuine, save a copy, and start gathering the information your business needs.

First, make sure the notice is genuine

Before you respond, confirm that the email really came from the vendor.
IMAGE SOURCE: https://www.pexels.com/photo/woman-using-laptop-while-talking-on-the-phone-7971729/  

Criminals sometimes take advantage of public breach announcements by sending fake password-reset emails or pretending to offer support. Someone who already uses the affected software is more likely to believe the message because the breach itself is real.

Avoid clicking links or calling numbers in an unexpected notice until you’ve checked it. Visit the vendor’s website by entering the address yourself, sign in through the customer portal you normally use, or contact a representative whose details you already have.

The UK National Cyber Security Centre recommends contacting an organization through details found on its official website when you’re unsure whether a message is genuine.

Once you’ve confirmed the notice, save the original message and any attachments. You may need them when speaking with your IT provider, insurer, legal adviser, or privacy contact.

Ask whether your business was affected

A breach at a software company doesn’t always affect every customer. The incident may have involved one product, database, office, or group of accounts.

Ask the vendor directly:
IMAGE SOURCE: https://www.pexels.com/photo/it-technician-working-in-data-center-server-room-37605911/

Was our account, company information, or user data affected?

If the vendor can’t give you a definite answer yet, ask whether your business is confirmed to be affected, possibly affected, confirmed not to be affected, or still under investigation.

That wording matters. “Still under investigation” does not mean your business is safe. It means the vendor has not finished checking.

Ask when you can expect a clearer answer and whether the vendor recommends taking any precautions while it investigates.

Find out what happened and when

The date the vendor announced the breach is only one part of the timeline.

Ask when the unauthorized activity began, when the vendor detected it, and when the affected systems were contained. If the vendor only knows an estimated date range, ask it to share that.

Those dates help your IT provider decide how far back to review your own records. You may need to check login activity, file transfers, account changes, invoices, payment instructions, or messages sent during the affected period.

You also need to understand what the unauthorized person was able to do.

Were they able to view information, copy it, change it, or delete it? Did they create new accounts, encrypt files, or use the vendor’s systems to contact customers?

The answer affects what you do next. Someone viewing a customer list creates a different risk from someone obtaining login credentials or gaining access to a system connected to your network.

Ask exactly what information was involved

A statement such as “customer information may have been affected” is too broad to guide your response.

Ask the vendor which information connected to your business was involved. Depending on the software, this could include employee or customer contact details, payroll information, payment records, identity documents, contracts, files, messages, support tickets, usernames, password hashes, login records, API keys, or security tokens.

Then ask whether all customers had the same information exposed.

Two businesses may use the same software in completely different ways. One company might use a platform only to store names and email addresses. Another might have uploaded contracts, identity documents, invoices, and payment information.

So the fact that both businesses use the same vendor doesn’t mean they face the same risk.

If the vendor says the information was encrypted, ask whether the encryption keys or any system capable of decrypting the information were also affected. Encryption can reduce the risk, but only if the attacker didn’t obtain what was needed to read the data.

Was the information viewed, copied, or simply present on an affected system?

This is where the vendor’s logs become important.

If the company says there is “no evidence” that your information was copied or misused, ask what records support that statement. You should also ask whether those records cover the entire period being investigated.

“No evidence of misuse” means the investigation has not found evidence. It doesn’t always mean the vendor can prove that nothing happened.

For example, the relevant logs may not have been retained for the full period, or they may not record every action an attacker could take. That doesn’t prove that data was stolen, but you should understand how much the vendor can confirm before deciding that no further action is needed.

Check passwords and connected systems

A password reset may be part of the response, but modern software often connects to other services without asking someone to enter a password each time.

Your vendor may use single sign-on, API keys, access tokens, security certificates, or integrations with your email, accounting, payment, file-storage, or backup systems.

Ask whether any of these connections were affected. Then ask which credentials need to be reset, revoked, or replaced.

Your IT provider should manage these changes where possible. Replacing the wrong key or disconnecting an integration without checking what depends on it can interrupt business systems or stop information from syncing.

If an employee used the same password for the breached service and another account, that password should be changed everywhere it was reused. A criminal who obtains one password can test it against email, banking, cloud storage, and other common services.

Ask what the vendor has done so far

A vendor may say that the breach has been contained. Usually, that means it has stopped the activity it knows about. The investigation and repair work may still be continuing.

Ask what the company has done to secure the affected systems.

Did it disable compromised accounts, revoke active sessions, patch a vulnerable system, rebuild affected servers, or replace exposed access keys? Has an independent security company reviewed the incident? And does the vendor currently consider the service safe to use?

You should also ask what work remains. Some early measures are temporary, so find out when the vendor expects to complete the permanent fixes.

NIST’s incident-response guidance explains that responding to an incident can involve several parties, including service providers, system owners, legal teams, and business leaders. Each party needs to understand what it is responsible for doing.

The vendor will handle its own systems. Your business may still need to protect its accounts, review activity, contact affected people, or meet contractual and legal requirements.

Find out what your business needs to do

Ask the vendor to give you customer-specific instructions in writing.

You may need to install an update, reset certain accounts, review activity logs, remove an integration, check recent transactions, or warn employees about related phishing attempts.

If an update is required, ask which versions of the software are affected and which version your business should now be using. Also confirm whether there is a deadline for completing the work.

Find out whether the attacker could use information from the breach to create convincing scams. Names, invoice details, support history, or the names of vendor employees could make a fraudulent message look genuine.

If the vendor has found related phishing emails, fake websites, or fraudulent support calls, ask it to share examples that you can pass to your staff.

Ask whether another company was involved

Software companies often rely on other providers to host systems, process payments, send emails, store backups, or run customer support. These other providers are sometimes called subprocessors.

If the breach happened at one of these companies, ask who it was, what service it provided, and what information it held. You should also find out whether it had direct access to your data or systems and whether the software vendor still uses it.

This information may be important even if you’ve never dealt directly with the other company. Your software vendor chose that provider and should be able to explain how the incident affected the service you use.

Agree on how you’ll receive updates

When an investigation lasts several days or weeks, getting information through a general support inbox can become frustrating. Each response may come from a different person, and you may have to explain the situation again.

Ask for a named contact or an incident response team that can answer follow-up questions. Confirm where official updates will be published and how often the vendor expects to provide them.

If the company doesn’t have new information yet, it should still be able to tell you when the next update will arrive.

Once the investigation is complete, ask for a final report. It should explain what happened, what information was involved, how the breach occurred, and what the vendor has changed since then.

The NCSC’s supplier security guidance recommends setting clear incident-reporting timescales, contacts, and responsibilities in supplier contracts. After the immediate response is over, check whether your existing agreement covers these points.

Keep a record of your response

Create a folder for the incident and keep the original notice, later updates, your questions, and the vendor’s answers.

You should also record what your business did, when each action was taken, who approved important decisions, and what advice you received from your IT provider, insurer, or legal adviser.

Having this information in one place makes it easier for everyone involved to work from the same facts. It also gives you a record of how your business assessed and handled the incident if questions come up later.

Privacy authorities in several countries require organizations to document certain breaches and their response. For example, the UK Information Commissioner’s Office says organizations should record the facts, effects, and remedial action taken.

Australia’s privacy regulator recommends a response based on containing, assessing, notifying, and reviewing the breach.

The exact requirements depend on where your business operates, what information was involved, and your role in handling that information.

Decide who else needs to be involved

The vendor’s notice may create responsibilities for your business as well.

Depending on what happened, you may need help from your IT provider, legal or privacy adviser, cyber insurer, senior management, or communications team. You may also need to contact affected customers, employees, regulators, or other organizations.

If the incident may be covered by cyber insurance, review your policy and notify your broker or insurer as required. Some policies require prompt notification or the use of approved legal, forensic, or incident-response providers.

If personal information was involved, get privacy or legal advice early. Notification requirements vary by location and may depend on the type of information, the likely harm, your contract with the vendor, and whether your business controls the information or processes it for someone else.

Under the GDPR, for example, a software provider acting as a data processor must notify the relevant controller without undue delay. The controller may still be responsible for assessing the breach and making any required notifications.

The European Data Protection Board’s guidance also explains that a vendor can provide information in stages as the investigation develops.

Frequently Asked Questions

What if the vendor says there is no evidence that our information was misused?

Ask what evidence and logs support that statement, whether those records cover the full period, and whether the investigation is complete. The answer may be reassuring, but you need enough detail to understand how the vendor reached it.

Should everyone change their password immediately?

Follow the vendor’s instructions and ask your IT provider which accounts are affected. If a password used with the vendor was also used elsewhere, change it on every affected account and stop reusing it.

Your IT provider should also check whether active sessions, API keys, or access tokens need to be revoked.

Does a vendor breach mean we must notify our customers?

Not always. It depends on whether your business was affected, what information was involved, where the affected people are located, your contracts, and the laws that apply.

Get appropriate privacy or legal advice before deciding.

Should we stop using the vendor?

A breach alone doesn’t automatically mean you should leave. Look at what happened, how much information was exposed, how the vendor responded, and whether the original problem has been fixed.

Pay attention to the quality of the vendor’s communication as well. If it repeatedly avoids reasonable questions or cannot explain how it has secured the service, you may need to reconsider whether you’re comfortable trusting it with your data

Sources and Further Reading

If a software vendor has reported a breach and you’re unsure what it means for your business, speak with your IT provider. If you don’t have one, you can always reach out to us and we’ll help you work through it.

—

Featured Image Credit

This Article has been Republished with Permission from The Technology Press.
Free A woman appears stressed while working on a laptop in her modern office. Stock Photo

How Hackers Keep Access to Your Email After You Change the Password

Summary: Changing the password blocks someone from signing in with the old password. However, they may still have an active session, a forwarding rule, access through a connected app, mailbox permissions, or a recovery method they added.

When someone gets into a business email account, changing the password should happen immediately. Once that is done, the account still needs a full check because other forms of access may remain.

During the time they had access, the attacker may have created a forwarding rule, approved a connected app, added a sign-in method, or granted access to another account. They may also have a browser or email app that is still signed in.

Email deserves particular care because it is connected to so many other services. Password-reset messages for accounting software, cloud storage, social media, and other business systems often arrive by email. Someone who can still read the inbox may be able to reach those accounts too.

That is why current recovery guidance from Microsoft, Google, and the UK National Cyber Security Centre includes several checks beyond changing the password.

Why a New Password May Not Remove Every Form of Access

Email services use sessions so you do not have to enter your password every time you open a message. After you sign in, the service gives your browser or email application a cookie or token that confirms the login has already been approved.

The service can continue accepting that session until it expires or is revoked. This means someone who signed in before the password changed may stay connected for a period of time, depending on the provider and the type of session.

The providers handle password changes differently. Google says that changing a password signs the user out in most places, but it lists exceptions that can include some devices and third-party applications. Google Workspace administrators also have separate controls for suspending an account and resetting its sign-in cookies.

Microsoft takes a similar approach for business accounts. Its guidance tells administrators to disable the affected account during the investigation and revoke active sessions separately.

The password change also leaves mailbox settings in place. A forwarding rule, delegate, or recovery method added while the account was compromised will remain until someone finds and removes it.

An Existing Session May Still Work

An active session is one of the first things your IT provider should check.

IMAGE SOURCE: https://www.pexels.com/photo/smartphone-screen-showing-account-verification-alert-33440144/  

If the attacker signed in through a browser or email application, that session may still hold a valid token. Malware on an employee’s computer can also steal a session cookie and send it to someone else.

A stolen cookie may allow the attacker to use a session that has already passed the normal login checks. In that situation, they may not need to enter the new password.

The administrator should use the email provider’s tools to revoke the account’s active sessions and tokens. The exact name of the control varies between services. It may appear as “revoke sessions,” “reset sign-in cookies,” “sign out everywhere,” or “log out of all devices.”

If malware may be present on the employee’s computer, use another device to begin the recovery process. The affected computer should be checked before the employee signs in again.

Forwarding Rules Can Keep Sending Out Your Email

After closing the active sessions, check what was changed inside the mailbox.

An attacker can create a forwarding rule that sends a copy of every new email to another address. They may also use a filter that only forwards messages containing terms such as “invoice,” “payment,” “bank,” or “password reset.”

More selective rules are harder to notice because most email continues arriving normally. The attacker only receives the messages they are interested in.

Rules can also hide activity. For example, a rule may move security warnings, customer replies, or questions about a payment request into a folder the employee rarely checks.

Both Microsoft and Google tell users and administrators to check forwarding settings and mailbox rules after a suspected compromise.

Microsoft 365 administrators should perform this check through the administration tools, not only from the employee’s Outlook settings. Microsoft specifically recommends reviewing all inbox rules, including hidden ones.

A Connected App May Have Permission to Read the Mailbox

Forwarding rules are one way to keep receiving email. A connected application can provide another.

Image Source: https://www.pexels.com/photo/creative-photo-of-a-lock-key-16564254/

Businesses commonly connect email accounts to scheduling tools, customer management systems, mobile email apps, document services, and browser extensions. These connections often use OAuth.

When a user approves an OAuth request, the application receives permission to access certain parts of the account. The application does not need to store the user’s password.

Attackers can misuse this process by creating an application that looks genuine and asking the user to approve it. Microsoft explains that a harmful app consent grant can provide access to email, files, contacts, and forwarding rules.

Some app connections may stop after a password reset, while others need to be removed separately. Review every application connected to the account and remove anything the business does not recognize, use, or approve.

An application’s name and logo do not confirm who created it. Your administrator should check the company behind it and the exact permissions it received.

Someone Else May Have Mailbox Permissions

Business email platforms allow one person to access another person’s mailbox. An executive may give an assistant access, for example, or several employees may work through a shared mailbox.

This type of access is called delegation. A delegate signs in with their own account, so changing the mailbox owner’s password does not automatically remove the delegate.

Exchange Online supports Full Access, Send As, and Send on Behalf permissions. Gmail also supports delegated mailbox access.

Check every person and group with access to the mailbox. Confirm why they need it and remove any permission that the account owner or administrator cannot explain.

Sending permissions need attention too. Someone with “Send As” access may be able to send messages that appear to come directly from the mailbox, even if they cannot read its contents.

Check Recovery and Sign-In Methods

The attacker may have added a phone number, recovery email address, authenticator app, passkey, or security key while they controlled the account.

A recovery method could help them regain access later. An authentication method might also allow them to approve another sign-in without knowing the new password.

Microsoft tells administrators responding to a compromised mailbox to review the user’s registered MFA devices and remove anything suspicious. Google also advises users to check recovery details, recent security activity, devices, and sign-in methods.

Compare every entry with the account owner. Remove anything that neither the employee nor the administrator recognizes.

How to Secure a Compromised Email Account

Some of the settings involved are only visible through the business administration tools. Contact your IT provider or email administrator rather than asking the employee to handle the entire cleanup from their inbox.

Disable or Suspend the Account

The administrator may temporarily disable or suspend the account while checking it. They should also revoke active sessions and tokens so the attacker is signed out.

The employee may lose access for a short time, but leaving the account active gives the attacker more time to read, send, or delete email.

Change the Password

Set a password that has not been used for another account. If the employee reused the old password elsewhere, those accounts need new passwords as well.

Do not send the new password to the affected mailbox. Use a phone call, an approved password manager, or another method your business trusts.

Some older applications use separate app passwords. Microsoft’s current guidance notes that these are not automatically revoked when the main password changes, so your administrator should remove or replace them if they are present.

Review the Mailbox and Account Settings

Check forwarding addresses, inbox rules, filters, blocked addresses, delegates, sending permissions, signatures, automatic replies, and connected applications.

Then review the registered devices, phone numbers, recovery addresses, authenticator apps, passkeys, and security keys.

POP and IMAP access should also be checked. Some businesses still use these settings for approved email applications, so confirm how the account is used before disabling them.

Find Out What Happened

Once access has been removed, work out what the attacker did while they were inside.

Check the Sent, Deleted, Drafts, Junk, and Archive folders. Look for messages the employee did not write, replies they did not see, password-reset emails, and changes to payment instructions.

The administrator should review sign-in logs, audit records, email traces, and security alerts. Start the search before the first known warning because the original compromise may have happened earlier.

A login from an unfamiliar location does not prove that someone else used the account. Mobile networks, VPNs, and internet providers can affect location data. The device, time, IP address, application, and activity around the login provide more useful context when considered together.

Contact Anyone Who May Have Received a Fraudulent Message

If the account sent false messages, contact the recipients through a trusted channel. Tell them which messages were not genuine and whether they need to change a password, delete a file, or ignore a payment request.

Pay particular attention to messages involving bank details, invoices, payroll, gift cards, or password resets.

If money may have been sent to the wrong account, contact the bank or payment provider immediately. Use a phone number from its official website or your existing records rather than one found in the email conversation.

Secure the Account Before Returning It to the Employee

Once the unknown access, settings, and permissions have been removed, the administrator can return the account to the employee.

Require MFA before the employee signs in again. Where the email platform supports them, passkeys and physical security keys provide better protection against phishing than codes that can be entered into a fake login page.

MFA helps prevent another login with a stolen password. The earlier checks are still required because MFA does not remove existing forwarding rules, delegates, connected apps, or recovery methods.

How to Reduce the Risk of Another Compromise

Ask your IT provider to block automatic forwarding to outside addresses unless your business has a reason to allow it. Microsoft 365 and Google Workspace also provide controls for limiting which third-party applications employees can connect.

Require MFA for every email account, especially administrators and employees who handle payments or sensitive information. Use passkeys or physical security keys where the platform supports them.

Employees should report unexpected MFA prompts, unfamiliar login alerts, mailbox changes, and messages sent from their account that they do not recognize. Report these signs as soon as they appear so your IT provider can check the account before more email is sent or deleted.

Frequently Asked Questions

Does changing an email password sign out every device?

It depends on the provider. Some services sign users out of most sessions after a password change, while others provide separate controls for revoking sessions and tokens. Follow the account-compromise instructions for the email service your business uses.

Can someone still receive my email after I change the password?

Yes. A forwarding rule or filter may continue sending them copies of your messages. Check all forwarding settings and mailbox rules.

Can an app access my email without knowing my password?

Yes. An app may receive permission through OAuth, which allows it to access approved account data without storing the password. Review and remove any connected application the business does not recognize.

Should I delete a compromised email account?

The account is usually disabled or suspended while it is secured and investigated. Deleting it could remove information your IT provider needs to work out what happened.

Is MFA enough to secure the account?

No. Local administ MFA helps prevent new sign-ins, but it does not remove mailbox rules, app permissions, delegates, recovery methods, or active sessions that already exist. Those need to be checked separately.

Sources and Further Reading

If you think someone still has access to your business email, contact your IT provider immediately. If you do not have an IT provider, you can always reach out to us and we’ll help you.

—

Featured Image Credit

This Article has been Republished with Permission from The Technology Press.
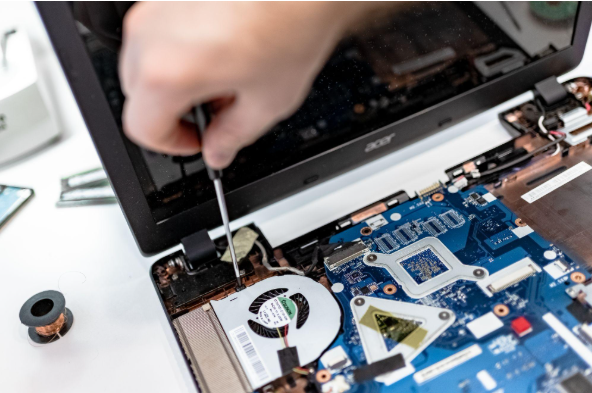
computer being repaired

How Long Business Computers Last and When to Replace Them

Summary: Three to five years is a practical replacement range for many business computers. The right time depends on security support, reliability, performance, warranty coverage, repair costs, and the employee’s work. Replace any computer that cannot run a supported operating system or the software your business requires.

Most business computers do not fail all at once. A laptop may still handle email and documents but take longer to start, struggle during video calls, or run out of battery halfway through the day.

For many office computers, three to five years is a sensible replacement range. Start reviewing each device when it reaches three years old, then decide whether it should be replaced soon or kept for another year or two.

Some computers will need to be replaced sooner because they cannot install a supported operating system, no longer run important software properly, or require frequent repairs. Others may remain useful beyond five years, especially in roles that only involve light office work.

Age helps you plan, but the computer’s security, condition, and suitability for the employee should determine when it is replaced.

Start Reviewing Computers After Three Years

Business computer manufacturers often base their lifecycle planning on replacement periods of around three or four years. Intel’s current refresh program allows employees using computers older than three years to select a replacement suited to their work, while Dell recommends refreshing business computers every three to four years.

These are planning recommendations rather than fixed expiry dates. A secure, reliable three-year-old laptop does not need to be replaced because of its age alone.

The three-year point is a good time to review the warranty, operating-system support, battery condition, repair history, and the employee’s current requirements. If the computer is likely to remain suitable for another year, record the next review date. If several problems have already appeared, include it in the next replacement order.

Reviewing computers after three years gives the business time to budget and avoids replacing several devices at once.

Security Support Comes First

Before looking at speed or battery life, confirm that the computer can run an operating system that still receives security updates.

Once an operating system reaches the end of support, newly discovered vulnerabilities may no longer be fixed. Security software can still provide some protection, but it cannot correct every weakness in the unsupported operating system underneath it.

The Australian Cyber Security Centre’s current system-management guidance says unsupported operating systems and networked equipment should be removed or replaced. The UK National Cyber Security Centre also recommends replacing obsolete products because continuing to use them increases the risk of compromise.

A computer can be physically reliable and still need replacement because its hardware cannot support a current operating system. In that situation, replacing the hardware is usually safer than continuing to use an unsupported system.

Some software companies offer temporary extended security programs after normal support ends. These programs can give a business more time to complete a planned replacement, but they do not extend the computer’s life indefinitely.

Ask your IT provider to check the support status of every operating system at least once a year. They should also confirm that the computers meet the requirements for future versions before the current one reaches its support deadline.

Match the Computer to the Employee’s Work

An employee who mainly uses email, documents, and browser-based applications may be comfortable using an older computer. Someone working with large spreadsheets, design files, video, engineering software, or several applications at once may need more recent hardware.

Review performance while the employee is completing normal work. A computer may need attention if applications regularly take too long to open, video calls become unstable, or the employee has to close programs before opening another one.

Ask the employee how often the computer interrupts their work. A slow startup once a week is different from delays that happen throughout the day.

Software requirements also change. Accounting systems, security tools, web browsers, and industry applications may stop supporting older operating systems or processors. Even if the application still opens, the software provider may no longer test or support that setup.

Check the hardware requirements before renewing an important application or moving the business to a new platform. This gives you time to identify which computers need an upgrade or replacement before the software changes.

Check the Cause Before Replacing a Slow Computer

Poor performance does not always mean the computer is too old.

A full storage drive, insufficient memory, unnecessary startup programs, malware, overheating, or a damaged operating system can all make a computer slow. A failing storage device may cause similar symptoms and should be dealt with quickly.

Ask your IT provider to identify the cause before approving a replacement. Maintenance, a software repair, additional memory, or a new storage drive may return the computer to normal performance.

The computer’s age and remaining support life still need to be considered. Spending money on an upgrade makes little sense if the device will soon lose operating-system support or if several other parts are already failing.

Include Reliability and Repair Costs

One repair may not justify replacing a computer, but repeated repairs change the calculation.

Unexpected shutdowns, failed updates, charging faults, damaged ports, storage errors, display problems, and recurring operating-system repairs can make a computer unreliable even when each individual issue seems manageable.

Review support requests by device. Add the repair bills, IT support charges, and the time the employee could not work normally. A repair that appears cheaper than a replacement may provide poor value if another problem is likely to follow.

The importance of the employee’s role also affects the decision. A failed computer can be particularly disruptive for someone who travels, meets customers, processes payments, or performs work that cannot quickly be moved to another device.

Keeping a prepared spare computer can reduce that downtime. The spare should still receive updates, run the required software, and be checked regularly.

Consider the Warranty and Availability of Parts

A computer does not automatically need replacement when its warranty expires, but the business becomes responsible for repair costs and may wait longer for service.

Review the warranty before it ends. Check whether an extension is available, what it covers, and how quickly the manufacturer will respond. Compare the price of extended coverage with the age and value of the device.

Manufacturers also limit how long they provide replacement parts and repairs. These periods differ by model, product type, and country, so check the policy for the exact computer rather than relying on a general rule for the brand.

Parts availability matters more when the business does not keep spare devices. A simple repair can still create several days of downtime if a component must be ordered.

A Battery Replacement May Extend a Laptop’s Life

Laptop batteries lose capacity with use and age. A device that once lasted most of the working day may eventually need to stay connected to a charger.

This may not affect an employee who works at a desk, but it can make the laptop unsuitable for someone who travels or works at customer locations.

Replacing the battery may be worthwhile if the computer remains supported, performs well, and is otherwise reliable. Check the full repair cost and whether parts are available before deciding.

Stop using a laptop if the battery is swollen, unusually hot, or changing the shape of the case. A damaged battery should be inspected and replaced by someone with the right equipment and experience.

Decide Whether to Upgrade or Replace

Some computers can be improved by adding memory, replacing storage, or installing a new battery. Others use parts that are difficult or uneconomical to replace.

An upgrade is reasonable when one component is causing the problem and the computer still has several years of security and software support ahead of it. Additional memory, for example, may help an employee who needs to keep several large applications open.

Calculate the complete upgrade cost, including parts, installation, data backup, and testing. Then compare it with the cost and expected life of a replacement.

A new computer will usually include a new warranty and may be easier for your IT provider to manage. An upgrade may still be the better choice when it solves a specific problem at a reasonable cost.

Older Computers Can Be Used in Less Demanding Roles

A computer that no longer suits one employee may still be suitable for another role.

A device used for design or data work could be reassigned to an employee who mainly uses email and browser-based applications. It must still receive security updates, run the required software, and remain reliable.

Before reassigning it, remove the previous employee’s data and accounts. The computer should be reconfigured for the new user, updated, checked for faults, and added to the asset inventory under its new assignment.

Do not reassign a computer that is unsupported or already causing regular support problems. Moving it to another employee only delays the same replacement.

Create a Replacement Schedule

Keep a record of each computer’s purchase date, model, assigned user, warranty expiry, operating system, and expected review date.

When a computer reaches three years old, check whether it can continue receiving security updates, whether it still runs the required applications, and how often it has needed support. Review its battery, warranty, repair costs, and the employee’s workload at the same time.

Assign a planned replacement year based on those findings. Review the date again if the employee changes roles, software requirements increase, or the operating system’s support timetable changes.

Spreading purchases across several budget periods is easier than replacing a large group of computers in one year. It also gives your IT provider time to order, configure, and test the new equipment.

Standardizing on a small number of approved models can simplify the process. Employees can share compatible docks, chargers, and accessories, while your IT provider can maintain consistent security settings and prepare spare devices more quickly.

Different roles may still need different models. A general office computer will not necessarily meet the needs of someone working with video, design, or specialist technical software.

Prepare the New Computer Before Retiring the Old One

Back up or transfer the employee’s business data before removing the old computer.

Confirm that the new device has the required email, documents, bookmarks, applications, printers, and shared folders. Check that multifactor authentication and any specialist software are working before the employee starts relying on it.

Once the move is complete, remove the old computer from device management, security monitoring, backup systems, and trusted-device lists. Cancel or reassign licenses that were tied to it, then update the asset inventory.

Keeping an old computer for a short transition period may be useful. Leaving it connected and unmanaged for months creates more equipment for the business to maintain and secure.

Remove Business Data Before the Computer Leaves

Deleting files or removing the employee’s account does not guarantee that all business data has been erased.

Storage should be sanitized before a computer is sold, donated, recycled, returned, or discarded. The correct method depends on the storage technology, encryption, and sensitivity of the information.

NIST Special Publication 800-88 Revision 2, published in September 2025, provides current guidance on selecting appropriate data-sanitization methods.

The Australian Cyber Security Centre also recommends backing up required information, unlinking accounts, removing removable media, and erasing the device. Businesses handling particularly sensitive information should consider using a professional data-destruction service.

Keep a disposal record containing the computer’s asset number, serial number, disposal date, and the method used to remove its data.

Six Questions to Ask During a Computer Review

  1. Can the computer run an operating system that still receives security updates?
  2. Does it support the software the employee needs?
  3. Does it handle the employee’s normal workload without regular delays?
  4. Has it required repeated repairs or support?
  5. Is it still covered by a suitable warranty, or are parts readily available?
  6. Would an upgrade provide enough useful life to justify its cost?

If the computer fails the security or software-support checks, plan to replace it. For performance and repair issues, compare the cost of fixing the device with the likely cost of keeping it for another year.

Frequently Asked Questions

How many years should a business laptop last?

Three to five years is a practical planning range for many business laptops. Replace one sooner if it becomes unreliable, cannot receive security updates, or no longer meets the employee’s requirements. A supported laptop may remain useful for longer in a less demanding role.

Should every computer be replaced at the same age?

No. Review computers based on their condition and use. A laptop carried between customer sites every day may need replacement sooner than a desktop used occasionally for basic office work.

Is a slow computer always ready for replacement?

No. Low storage, insufficient memory, malware, overheating, or an operating-system problem may be responsible. Have the cause checked before deciding whether to repair, upgrade, or replace the computer.

Should a computer be replaced when its warranty ends?

Not automatically. Review its condition, support status, repair history, importance to the employee, and the availability of spare equipment. The end of the warranty is a suitable time to perform that review.

Can an old computer be kept as a spare?

Yes, provided it remains supported, reliable, updated, and properly managed. Check spare computers regularly and confirm that they can still run the software employees need.

Can a business sell or donate an old computer?

Yes, but all business data must be removed first. Use a suitable sanitization process and keep a record showing how and when the computer was disposed of.

Sources and Further Reading

Ask your IT provider to review the age, support status, and condition of your business computers. And if you don’t have an IT provider, feel free to reach out to us and we’ll help you sort it out.

—

Featured Image Credit

This Article has been Republished with Permission from The Technology Press.
two women with laptops

Small Business IT Budget: What to Include and How to Plan It

Summary: Your IT budget should include the technology you already use, the support required to maintain it, and the upgrades you expect to make during the year. It should also cover cybersecurity, backups, employee changes, planned projects, and a reserve for urgent repairs or replacements.

If your IT budget only covers computers, Microsoft 365, and the occasional repair, it is probably missing several costs.

Your business may also be paying for software subscriptions, cloud storage, backups, security tools, internet services, phone systems, websites, network equipment, staff training, and outside IT support.

Some of those costs appear every month. Others arrive once a year or only when equipment needs to be replaced. Without a complete budget, an annual renewal or failed computer can become an expense the business did not prepare for.

A detailed IT budget shows what you are paying for now, what will need to be replaced, and which improvements are planned for the year.

There Is No Standard IT Budget for Every Small Business

Online benchmarks often suggest spending a certain percentage of revenue on technology. That percentage may have little connection to what your business needs.

A ten-person law firm, a retailer, and a manufacturing business can have similar revenue but completely different systems. The number of employees, business locations, devices, cloud services, security requirements, and customer obligations all affect the budget.

Consider how much the business depends on each system. If losing internet access would stop customer payments, the internet connection needs more attention than it would in a business that can continue working offline. If employees work with sensitive financial or health information, security and compliance costs may be higher.

Calculate the cost of the systems your business needs first. Revenue-based benchmarks can then provide context, but they should not determine the budget.

Start With a Complete Technology Inventory

You cannot budget properly if you do not know what the business owns and pays for.

Create an inventory of computers, phones, tablets, printers, servers, network equipment, software, cloud services, websites, domains, backup systems, and phone services.

Record who uses each item, what it costs, when it renews, who manages it, and how important it is to the business. Include the supplier, contract term, billing frequency, and account owner.

The NIST Cybersecurity Framework 2.0 Small Business Quick Start Guide recommends maintaining an inventory of hardware, software, systems, and services. It also recommends recording the effect on the business if an important asset becomes unavailable.

Check invoices, company credit cards, bank statements, app stores, and department expenses. Software purchased directly by an employee may not appear in the main IT records.

The inventory may reveal duplicate services, licenses assigned to former employees, equipment that no longer receives updates, or subscriptions that no one uses.

Budget for Computers and Other Equipment

Include every physical device the business expects to purchase or replace during the year.

The cost of a new computer may also include monitors, docking stations, keyboards, headsets, webcams, carrying cases, warranty coverage, and delivery.

The device will need to be prepared before an employee can use it. Setup may include installing software, applying security settings, creating user accounts, transferring data, connecting printers, and testing access to business systems.

Other equipment may include mobile phones, tablets, printers, scanners, payment terminals, security cameras, wireless access points, network switches, firewalls, and battery backup units.

Keep a record of each device’s purchase date, warranty status, operating system, and expected replacement date. Replacing a planned number of computers each year is easier to budget for than waiting until several become unreliable at the same time.

Remember to include spare equipment. A prepared spare laptop can reduce downtime when a device is damaged or fails.

Old equipment also creates costs. Business data must be securely removed before a computer, phone, or storage device is sold, recycled, returned, or discarded.

Include Software and Cloud Subscriptions

List every subscription used by the business.

These may include email and productivity software, accounting systems, customer management platforms, industry-specific applications, electronic signature services, password managers, security software, backup services, cloud storage, device management, website hosting, and domain registrations.

Check whether each service is billed monthly or annually. Several annual renewals arriving in the same month can affect cash flow even when the monthly equivalent appears affordable.

Record the renewal date and current number of licenses. Remove licenses assigned to former employees, unused accounts, and duplicate services. Confirm whether the provider requires a minimum number of users or an annual commitment.

Allow for hiring during the year. A new employee may need more than an email license. They could also require security software, cloud backup, a business phone number, device management, and access to specialist applications.

Storage and usage charges also need attention. Some cloud services charge more when the business stores additional data, sends more messages, adds locations, or uses advanced features.

Review what is included in each subscription. Support, backup, security, data retention, and reporting may require a more expensive plan or a separate service.

Account for Employee Onboarding and Offboarding

A new employee may need a computer, accessories, software licenses, security tools, user accounts, phone services, and setup work. If the role is new, the business may also need additional storage, internet capacity, or specialist software.

When someone leaves, their access must be removed, company information transferred, equipment collected, and software licenses canceled or reassigned. The business may need to preserve email or files for operational, legal, or compliance reasons.

Contractors and temporary staff also create costs. Even when they use their own equipment, they may still need accounts, secure access, software, and support.

Estimate the expected number of new starters and departures during the budget period. Include both the technology and the work required to manage those changes.

Decide How You Will Pay for IT Support

Your business may use a managed IT provider, employ internal IT staff, pay for support when needed, or combine these approaches.

For managed IT services, confirm exactly what the monthly agreement covers. It may include help desk support, monitoring, software updates, device management, user administration, security tools, vendor support, and routine maintenance.

Ask which services are billed separately. Projects, after-hours work, office moves, major upgrades, equipment installation, and support for specialist applications may sit outside the regular agreement.

If you pay for support as needed, review the previous two or three years of invoices. Include emergency work, not just routine maintenance. Check how much was spent after equipment failures, account problems, internet outages, and security incidents.

Internal IT costs may include salaries, benefits, recruitment, training, certifications, and cover during holidays or illness. A single internal employee may still need outside help for specialist projects or serious incidents.

Set Aside Money for Cybersecurity

Cybersecurity spending should be clearly identified in the budget, even when some services are included in your software licenses or IT support agreement.

Your cybersecurity budget may include endpoint protection, email filtering, multifactor authentication, password management, device management, security monitoring, software updates, vulnerability checks, staff training, and incident-response planning.

The correct controls depend on the systems you use, the information you hold, and the damage a security incident could cause.

A business that stores customer payment details or confidential client records may need more protection than one that holds little sensitive data. Regulations, customer contracts, and cyber insurance requirements may also affect what must be implemented.

The NIST Cybersecurity Framework 2.0 covers six areas: governing cybersecurity risk, identifying important systems, protecting them, detecting incidents, responding, and recovering. Use those areas to check whether the budget covers more than preventive security software.

Not every small business needs every security product. Ask your IT provider to explain which controls are recommended, which risks they address, and whether they are already included in another service.

Include Backup and Recovery Costs

Budget for the entire backup and recovery process, not only the storage used to hold backup copies.

Costs may include backup software, cloud storage, isolated copies, monitoring, restore testing, and professional help during recovery.

Confirm what is being backed up. Important information may be stored on employee computers, servers, cloud platforms, accounting systems, websites, mobile devices, and specialist applications.

Do not assume every cloud service retains deleted or damaged information for as long as your business requires. Review the provider’s retention periods and recovery features. If those options do not meet your needs, include a separate backup service in the budget.

Backups also need to be tested. A successful backup notification shows that a task ran. A restore test confirms that the data can be recovered and used.

The UK National Cyber Security Centre recommends regularly backing up essential information and testing that it can be restored.

Allow for storage growth. If your business creates more files, emails, recordings, images, or customer records each year, backup costs may increase as well.

Budget for Internet and Network Equipment

Include your internet service, routers, firewalls, switches, wireless access points, cabling, and any support or security subscriptions attached to that equipment.

If losing internet access would stop the business from working, consider the cost of a backup connection. Compare that cost with the revenue, wages, and customer service time that could be lost during an outage.

Ask whether the backup connection uses a different type of service or supplier. Two connections may still depend on the same local infrastructure, which means one fault could affect both.

Review whether your current connection can support expected hiring, cloud applications, video calls, backups, and customer Wi-Fi. A service that works for ten employees may not be suitable after the business grows.

Network equipment requires software updates and eventual replacement. Record the support status of routers, firewalls, switches, and wireless access points. Equipment that no longer receives security updates should be scheduled for replacement.

Include installation and configuration costs. New equipment must be secured, connected to existing systems, documented, and tested before it is ready to use.

Include Phones and Communication Services

Phone and communication costs may be billed separately from other IT services, but they still belong in the technology budget.

Include business phone systems, mobile plans, phone numbers, call recording, voicemail, video conferencing, messaging, and contact-center services.

Check whether the service charges per user, phone number, call, recording, or storage amount. International calling, premium support, and additional features may create separate charges.

Include phones and headsets for new employees. If the business records calls, budget for the required storage, access controls, and retention settings.

Check when contracts end and whether equipment must be returned. Changing phone providers may also involve setup, number transfers, staff training, and temporary overlap between the old and new services.

Include Website, Domain, and Online Service Costs

These can include domain registration, website hosting, security certificates, website maintenance, software updates, plugins, backups, online forms, analytics, and email delivery services.

Confirm who owns the domain and website accounts. They should be registered to the business rather than an employee, contractor, or web developer.

Record domain renewal dates and enable appropriate renewal notifications. Losing control of a business domain can interrupt the website, email, and other services connected to it.

If the website accepts payments, bookings, or customer information, include the cost of maintaining its security and testing that it works.

Budget for Staff Training

Employees need training on the systems they use and the security risks they may encounter.

The budget may include cybersecurity awareness training, phishing simulations, training for new software, and instructions for employees who handle sensitive information or approve payments.

Training should also cover what employees must do when they receive a suspicious request, lose a device, send information to the wrong person, or notice unusual activity.

The Australian Cyber Security Centre’s Small Business Cyber Security Guide includes employee training and awareness as part of protecting a business from email attacks.

Include the time employees need to complete training. Even when the training platform is inexpensive, staff still need time during the working day to use it.

New systems may require additional training. Include that cost in the project budget instead of assuming employees will learn the software without support.

Allow for Compliance, Contracts, and Cyber Insurance

Your industry, location, customer contracts, or insurance policy may require specific technology and security controls.

Costs may include security assessments, audits, policy reviews, vulnerability testing, data-retention changes, access reviews, incident-response exercises, or independent certifications.

A customer may ask your business to complete a security questionnaire before signing or renewing a contract. Answering it may reveal controls that need to be introduced.

Cyber insurance applications may also ask about multifactor authentication, backups, endpoint protection, email security, employee training, and incident-response planning.

Review upcoming renewals and audits before approving the budget. This gives the business time to obtain quotes and complete required work.

Legal and compliance requirements differ between countries and industries. Confirm your obligations with the appropriate legal, compliance, insurance, and IT advisers.

Plan for Technology Projects

Keep planned projects separate from normal operating costs.

Projects may include moving offices, opening another location, replacing a server, changing phone systems, improving Wi-Fi, moving data to a new cloud service, or introducing a new business application.

Estimate the complete project cost. Include planning, licenses, equipment, implementation, data transfer, testing, training, temporary services, and support after launch.

Some projects require two systems to run at the same time while information is moved and employees are trained. Include that overlap in the budget.

Ask department managers what changes they expect during the year. A new service introduced by one department may require additional security, storage, integration, backup, and support work.

Business.gov.au recommends including both upfront and ongoing costs when preparing a digital budget. Check what the project will cost after the initial work is complete.

Review Supplier Contracts and Renewal Dates

Record the contract owner, renewal date, notice period, billing method, and cancellation process for each major supplier.

Some services renew automatically. Others require advance notice if you want to reduce licenses or cancel the agreement.

Check whether prices can change during the contract and whether the agreement includes minimum quantities. If the business expects to reduce staff or stop using a system, make sure the contract allows the licenses to be reduced.

Confirm how data can be exported and what happens when the service ends. A cheaper replacement may still involve migration, setup, training, and temporary overlap costs.

Do not leave important technology accounts tied to one employee’s personal email address or payment card. The business should retain access if that person leaves.

Keep a Reserve for Unplanned Costs

A laptop may be damaged, a firewall may fail, an employee may need urgent replacement equipment, or a technical problem may require work outside the support agreement.

There is no reserve percentage that suits every business. Base the amount on realistic costs, such as replacing an essential computer, obtaining emergency support, or restoring an important service.

Review unplanned IT spending from previous years. Use those figures when deciding how much to set aside.

The reserve should be separate from planned replacements. A computer already scheduled for replacement is not an unexpected cost.

Separate Recurring Costs From One-Time Costs

Recurring costs include software subscriptions, support agreements, internet services, phone systems, backup services, security tools, and equipment leases.

One-time costs include new equipment, migrations, office moves, installation work, and major upgrades.

Record annual subscriptions separately from monthly ones so that the business knows when larger payments are due.

You may also need to separate operating expenses from capital purchases for accounting and tax purposes. The rules vary by location, so confirm the correct treatment with your accountant.

How to Build Your Small Business IT Budget

  1. Create an inventory of your hardware, software, services, suppliers, and contracts.
  1. Record current monthly and annual costs, renewal dates, and notice periods.
  2. Identify equipment that needs to be replaced during the budget period.
  3. Estimate hiring, departures, new locations, and other business changes.
  4. Add support, cybersecurity, backup, training, compliance, and recovery costs.
  5. Create separate budgets for planned technology projects.
  6. Add a reserve based on realistic emergency support and replacement costs.
  7. Review the completed budget with your IT provider and accountant.

Record who approved each item and who is responsible for managing it. Review actual spending during the year instead of waiting until the next annual budget.

Review the Budget During the Year

Check the budget at least every quarter.

Compare actual invoices with the amounts expected. Look for new subscriptions, unused licenses, supplier price changes, additional storage charges, and projects that cost more or less than planned.

Update the forecast when the business hires employees, changes locations, introduces new services, or signs a contract with new security requirements.

A quarterly review also gives you time to plan for upcoming annual renewals. It is easier to compare providers or change services when the renewal deadline is still several months away.

Frequently Asked Questions

How much should a small business spend on IT?

There is no reliable percentage for every small business. Calculate the cost of the equipment, services, security, support, and projects your business needs. Industry benchmarks can provide context, but they should not replace a budget based on your operations and risks.

Should cybersecurity have a separate budget?

Cybersecurity costs should be clearly identified, even when some are included in software licenses or an IT support agreement. This makes it easier to see which protections are funded and which improvements still require approval.

How often should the IT budget be reviewed?

Review it at least annually when preparing the budget and quarterly during the year. Update it after significant hiring, office moves, new systems, supplier changes, or new compliance requirements.

Should equipment purchases and monthly services be combined?

Include both in the overall IT budget, but record them separately. This makes recurring operating costs easier to distinguish from one-time purchases and projects.

What costs are commonly left out of an IT budget?

Setup work, employee onboarding and offboarding, backup testing, staff training, security reviews, equipment disposal, project work, subscription increases, and urgent replacements are commonly overlooked.

Who should prepare the IT budget?

The business owner or finance team should work with the person responsible for IT. Department managers should also provide information about hiring, new software, planned projects, and changes to business operations.

Sources and Further Reading

Ask your IT provider to review the budget before you approve it. And if you don’t have an IT provider, feel free to reach out to us and we’ll help you sort it out.

—

Featured Image Credit

This Article has been Republished with Permission from The Technology Press.